Security & privacy
Fewer third parties, by design
Security and privacy are at the core of what we do. In practice that has meant refusing several things that would have been easy to add.
The reasoning
You may have noticed there is no like button
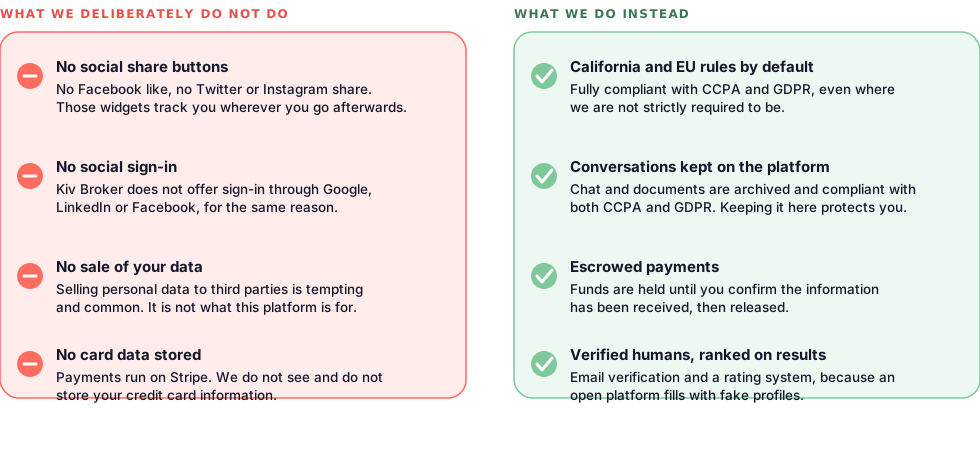
No link to like on Facebook, no share on Twitter, no Instagram widget.
You may, or may not, know that as you put that little logo at the bottom of the page, your information is tracked wherever you go — forever. Those ad-tech companies exist to serve one purpose: to track you everywhere, whether you know it or not, whether you even have an account with them or not. And to serve you annoying ads.
Kiv Broker does not offer sign-in through Google, LinkedIn or Facebook, for those reasons.
While it is very tempting to make money through the sale of your personal data to third parties, this is not what Kiv Broker is all about. We are 100% compliant with California and European Union rules and regulations, even if we do not have to be.
Payments
Subscription payment is secure and runs on Stripe, the largest and most widely used API today. We do not see and do not store your credit card information.
Conversations
Keep discussions on Kiv Broker. The chat system is secure and compliant with both CCPA in California and GDPR in Europe, and discussions and documents are archived.
Escrow
Where a payment is owed to a counterparty, we keep the funds in escrow until you tell us the information has been received by you.
Infrastructure
Built on AWS, with the security work done in advance
The platform is described as meeting the industry's most stringent security requirements, which is a threshold set by insurance carriers rather than by software buyers.
- HostingAWS-based infrastructure
- AvailabilityHigh availability, any time
- ScalingAutomatic, with no downtime
- PaymentsStripe
- FrameworksCCPA and GDPR addressed in the policy
What a security review usually asks
- Where is data hosted, and who can reach it
- How are payment credentials handled — answer: they are not, Stripe holds them
- Is there a data processing agreement, and what does it say about sub-processors
- What happens to data on termination
- Which jurisdictions' rules apply to each user
Data we collect
What the platform asks for, and why
The published privacy policy lists the categories of personal data the platform collects, by itself or through third parties.
Purposes of processing
The published policy states that data is collected to provide the service, comply with legal obligations, respond to enforcement requests, protect rights and interests, and detect malicious or fraudulent activity — and additionally for:
- Registration and authentication provided directly by the platform
- Handling payments
- Hosting and back-end infrastructure
- Infrastructure monitoring
- Managing contacts and sending messages
- Interaction with support and feedback platforms
- Analytics
Questions
Security and privacy questions
Questions we have not answered?
Send them to us — security questions are the ones worth asking before you sign up, not after.